Best VPN for Healthcare

Ask any VPN company for a signed business associate agreement (BAA) before patient data crosses it. Of the business VPNs we checked, only some say they will sign one, and the terms differ by plan.

A traveler working on a laptop at an airport window at dawn

Question 1 of 2

What is behind the search for a VPN for your practice?

20,024 VPN picks made through VPN.com in the last 30 days

What the rule asks of you

What HIPAA asks of a practice that uses a VPN

When does a VPN company need to sign a BAA?

A business associate agreement (BAA) is the contract HIPAA requires between a practice and a company that handles patient data for it. HHS says a business associate is a person or company that performs services for a covered entity that involve creating, receiving, maintaining or transmitting protected health information.

HHS also describes a narrow "conduit" exception for services that only transmit information and see it only in passing. For cloud services, HHS limits that exception to transmission-only services, with any storage temporary and incidental to the transmission. We found no HHS statement that settles which side of that line a VPN service falls on, so treat the question as open and ask your counsel.

  1. When in doubt, ask for the BAA.For cloud services that hold patient data on your behalf, HHS says the practice must have a BAA in place first. If a vendor will not put its position in writing, do not send patient data through it.
  2. Ask before you buy.The BAA you can get depends on the plan. The table below shows what each vendor says about it.

General information, not legal advice. A VPN alone does not make a practice HIPAA compliant: HHS does not certify products, and compliance covers your policies, risk analysis, vendor contracts and training.

What a VPN covers, and what it does not

  1. Covers: data in transit.The Security Rule asks you to guard patient data sent over a network. It lists encryption in transit as "addressable" and says to encrypt whenever deemed appropriate (45 CFR 164.312). A VPN is one way to do that.
  2. Does not cover: the risk analysis.The rule requires an "accurate and thorough" assessment of risks to patient data (45 CFR 164.308). No product does that for you.
  3. Does not cover: audit controls.The rule asks for ways to record and examine activity in systems that hold patient data. Ask your counsel whether a VPN’s logs, or a no-logs promise, matter to that duty.
  4. Does not cover: everything else.HHS says encryption alone cannot adequately safeguard patient data, because it does not address integrity, availability, risk analysis or physical safeguards.

A VPN alone does not make a practice HIPAA compliant. It is one technical safeguard inside a programme you run.

By plan

Which plans say they sign a BAA

Read from each vendor’s own pages on 8 October 2026; NordLayer, Cloudflare and Proton were read again on 29 October 2026. A vendor’s page shows what the vendor says, not what it will agree to in a contract.

What you are comparingBAA, as the vendor saysControls, as the vendor says
NordLayerSays it signs a BAA only with customers on annual or longer billing. Monthly plans are not eligible, and no patient data may go through it until the BAA is signed.Says Core and above can add a dedicated-IP server (extra monthly fee) and IP allow-listing; Lite cannot. Lists SSO and MFA.
Proton VPN for BusinessSays it offers BAAs to all Proton users. We could not confirm from public pages that the VPN is in scope, so ask.Says Professional includes dedicated IPs and SSO, and Essentials enforces 2FA.
Cloudflare Zero TrustSays it signs BAAs only with enterprise customers.Says dedicated egress IPs are an Enterprise add-on.
Surfshark VPN for TeamsWe found no BAA statement on its pages.Says a dedicated IP is not a feature of VPN for Teams.
ExpressVPN for TeamsWe found no BAA statement on its pages.Says a dedicated-IP add-on is available on 1- or 2-year Teams plans; SSO and MFA not stated.

The risk, in numbers

Patient data is a steady target.

The rules ask what you did to protect it.

663
large breaches of patient data (500 or more people) reported to HHS for 2024
81%
of those large breaches were hacking or IT incidents

Source HHS Office for Civil Rights, 2024 Report to Congress on the Breach Notification Program

Our verdict

Get the BAA in writing before patient data crosses it

Our take: NordLayer is our pick to start with. It says it signs a BAA, on annual or longer billing only, and it lists SSO and MFA. A VPN alone does not make a practice compliant, so ask for the BAA in writing first.

  • Says it signs a BAA on annual or longer billing. Monthly plans are not eligible.
  • Says no patient data may go through it until the BAA is signed.
  • One admin console to add and remove people, with SSO and MFA listed.
  • A dedicated-IP server on Core and above, for an extra monthly fee.
NordLayer
  • G2 4.3/5Reviews: 126 · As of October 2026
  • Gartner Peer Insights 4.6/5Ratings: 104 · As of October 2026
  • Easy team rollout
  • Reliable connections
  • Every device encrypted

Why NordLayer is where we would start:

  • Says it signs a BAA on annual or longer billing
  • Lists SSO and MFA
  • Admin console to add and remove people

What NordLayer says about its BAA:

  • Annual or longer billing only
  • Monthly plans are not eligible
  • No patient data until the BAA is signed

Controls NordLayer says depend on the plan:

  • Dedicated-IP server and IP allow-listing: Core and above
  • Lite cannot add either
  • Four plans: Lite, Core, Premium and Enterprise

The full guide

The detail behind our pick

Bottom Line: Ask any VPN company for a signed business associate agreement (BAA) before patient data crosses it, and expect the answer to depend on your plan: NordLayer says it signs one only on annual or longer billing, and Cloudflare says only with enterprise customers. A VPN alone does not make a practice HIPAA compliant.

What this page is for

This page is for a practice manager or owner choosing a business VPN. It sits under our best VPN for business guide, which covers what a business VPN is and how it differs from a personal one. For larger organisations see the enterprise VPN guide, and for the general privacy picture the data protection guide. Law firms face a different rule; see best VPN for law firms.

We do not run our own security tests. Everything vendor-specific below is what the vendor says on its own pages, with the date we read it, and HHS and federal regulation text are linked under Resources. This is general information, not legal advice.

Is there a HIPAA compliant VPN?

No. HHS says the Office for Civil Rights does not endorse, certify or recommend specific technology or products, so no VPN carries a government HIPAA certification. Cloudflare’s own page makes the same point: HHS does not recognize a certification for HIPAA compliance. A vendor can sign a BAA and offer controls that support your programme. A VPN alone does not make you compliant.
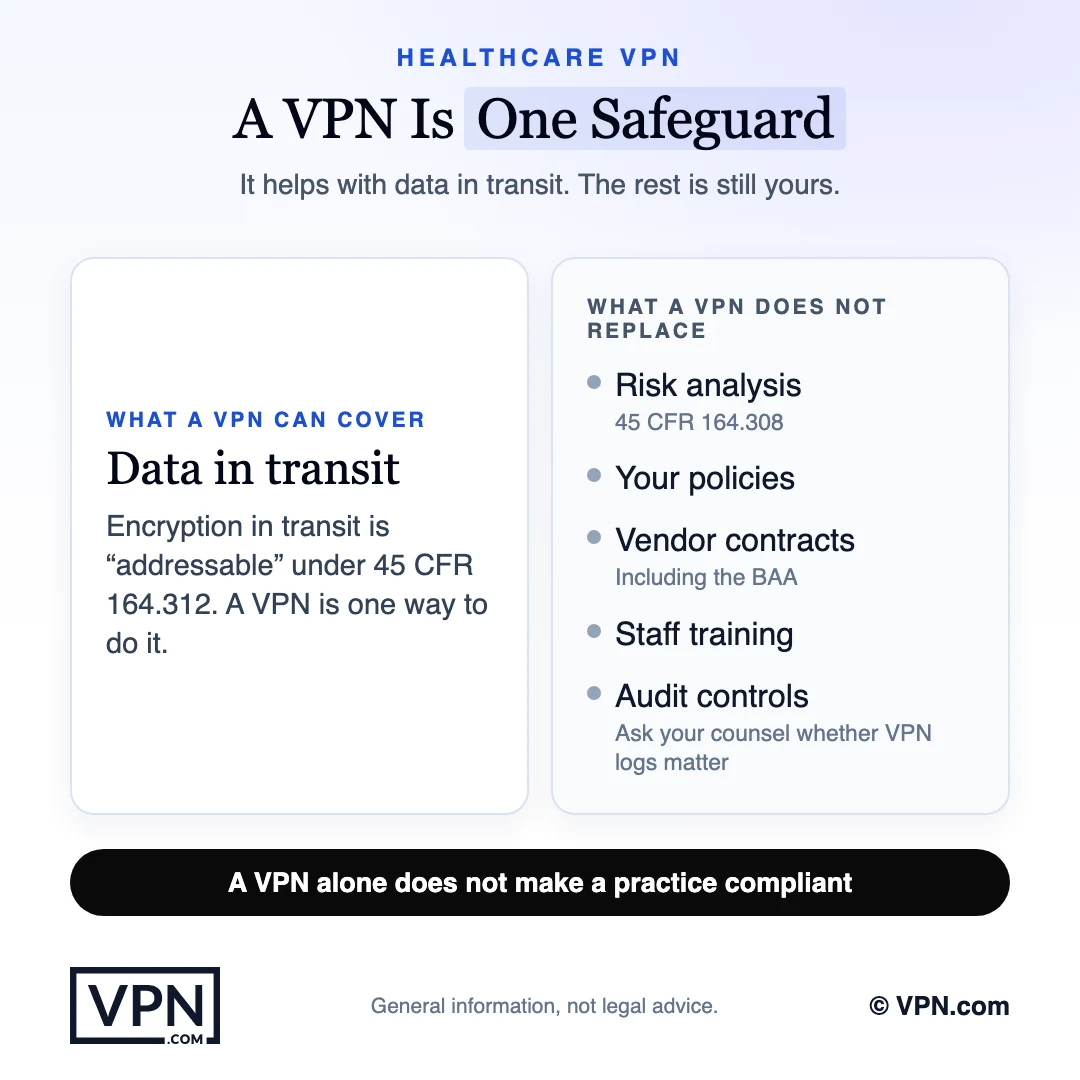
Two columns: a VPN can cover patient data in transit, but it does not replace the risk analysis, your policies, vendor contracts including the BAA, staff training or audit controls

What to ask a VPN company before patient data crosses it

  1. Will you sign a BAA, and on which plan and billing term? Get the answer in writing. NordLayer says it will not sign on monthly billing.
  2. Is the VPN product itself covered by the BAA? A company can sign a BAA for one product and not another. Proton, for example, says it offers BAAs to all users, but we could not confirm from public pages that the VPN is covered.
  3. Which controls come with my plan? Dedicated IP, single sign-on (SSO) and multi-factor sign-in (MFA) are gated by plan at the vendors below.
  4. What happens before the BAA is signed? NordLayer says patient data may not go through it until the BAA is executed, so a monthly trial is for testing without patient data.
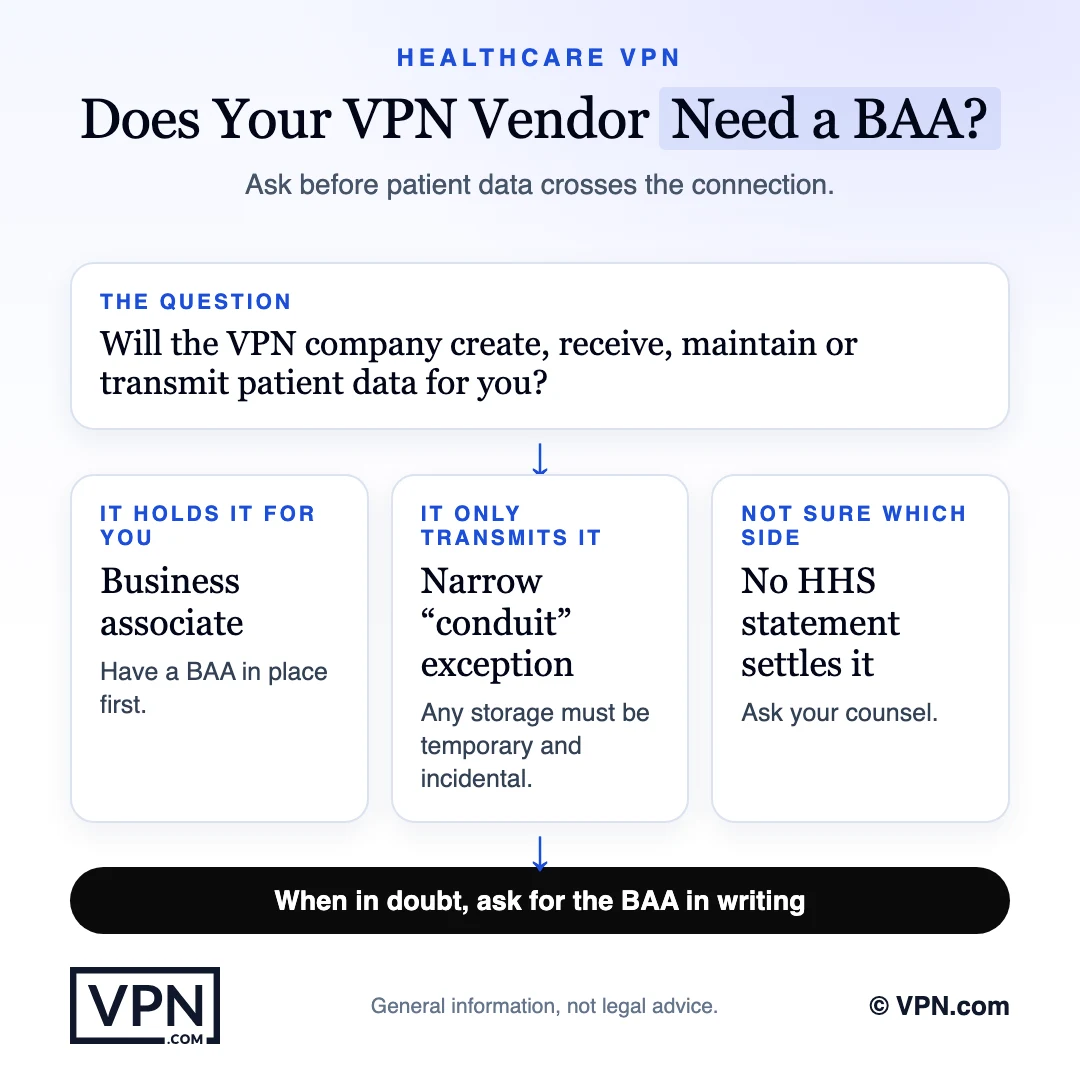
Decision flow: will the VPN company create, receive, maintain or transmit patient data for you. If it holds the data, it is a business associate and a BAA comes first. If it only transmits, a narrow conduit exception may apply. If unsure, ask for the BAA in writing and ask your counsel

Which plans say they sign a BAA

Every row is what the vendor says on its own pages, read on 8 October 2026, with NordLayer, Cloudflare and Proton read again on 29 October 2026. A vendor page is evidence of what the vendor says, not of what it will sign.

ProviderWhat it says about a BAAPlan or term conditionSource
NordLayerSigns a BAAAnnual or longer billing onlyNordLayer help centre[1]
Proton VPN for BusinessOffers BAAs to all Proton usersVPN scope not confirmedProton for Business[2]
Cloudflare Zero TrustSigns BAAsEnterprise customers onlyCloudflare[3]
Surfshark VPN for TeamsNo statement foundNot statedn/a
ExpressVPN for TeamsNo statement foundNot statedn/a

Cloudflare has no review page on VPN.com, so it is not linked internally. NordLayer has no review page either, so NordLayer links to its own site through our partner link. We earn a commission if you buy NordLayer through it; that does not change what its pages say.

Final Verdict

If this is your situationStart the conversation with
You want a BAA on a standard business planNordLayer on annual billing, or Proton for Business. Ask each to confirm in writing that the VPN product is covered
You already hold an enterprise contract with a network vendorCloudflare, which says it signs BAAs only with enterprise customers
You need a dedicated IP on a small planNordLayer Core or above, or Proton Professional, as each vendor says
A vendor will not confirm its position in writingDo not send patient data through it

Whatever you pick, the VPN is one safeguard. Your risk analysis, staff training and vendor contracts are what a regulator asks about.

References

  1. Nordlayer. n.d. NordLayer help centre. https://help.nordlayer.com/docs/nordlayer-hipaa-baa.
  2. Proton. n.d. Proton for Business. https://proton.me/business/healthcare.
  3. Cloudflare. n.d. Cloudflare. https://www.cloudflare.com/trust-hub/us-privacy-compliance/.
  4. HHS. n.d. HHS: 2024 Report to Congress on the Breach Notification Program. https://www.hhs.gov/sites/default/files/breach-report-to-congress-2024.pdf.
  5. HHS. n.d. HHS: Guidance on HIPAA and Cloud Computing. https://www.hhs.gov/hipaa/for-professionals/special-topics/health-information-technology/cloud-computing/index.html.
  6. HHS. n.d. HHS: Are the US Postal Service and similar couriers business associates? https://www.hhs.gov/hipaa/for-professionals/faq/245/are-entities-business-associates/index.html.
  7. ECFR. n.d. 45 CFR 164.312, technical safeguards. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-C/section-164.312.
  8. ECFR. n.d. 45 CFR 164.308, administrative safeguards. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-C/section-164.308.
  9. Nordlayer. n.d. NordLayer pricing. https://nordlayer.com/pricing/.

Frequently Asked Questions

Does a VPN company need to sign a business associate agreement with a medical practice?

It depends on whether the VPN company counts as a business associate. HHS defines one as a company that creates, receives, maintains or transmits patient data on a practice’s behalf, and limits the “conduit” exception to transmission-only services. We found no HHS ruling on VPNs, so when in doubt, ask for the BAA. This is not legal advice.

Is there such a thing as a HIPAA compliant VPN for healthcare?

No. HHS says it does not endorse, certify or recommend specific technology products, so no VPN holds a government HIPAA certification. A vendor can sign a BAA and offer supporting controls, but a VPN alone does not make a practice compliant. Treat “HIPAA compliant VPN” as a marketing phrase.

Which VPN providers say they will sign a BAA, and on which billing plan?

Of the business VPNs we checked, NordLayer says it signs only on annual or longer billing, Proton says it offers BAAs to all Proton users, and Cloudflare says it signs only with enterprise customers. We found no BAA statement for Surfshark’s or ExpressVPN’s team plans. Read on 8 and 29 October 2026.

Can a practice start on a monthly plan and sign the BAA later?

Not for real patient records. NordLayer says BAAs are unavailable on monthly plans and that no patient data may go through its service until one is signed. A monthly plan can work for testing with no patient data. Check your own vendor’s terms before you load anything real.

Does HIPAA require a VPN for a medical practice?

No. HHS says the HIPAA Rules do not endorse or require specific types of technology. The Security Rule lists encryption of data in transit as addressable, to use whenever deemed appropriate (45 CFR 164.312). Whether a VPN is how you do that is a risk-analysis decision. A VPN alone does not make you compliant.

Do a practice’s VPN logs matter for HIPAA audit controls?

The Security Rule asks for ways to record and examine activity in systems that hold patient data (45 CFR 164.312). Whether a VPN’s logs, or a no-logs promise, matter to that duty is a question for your risk analysis and counsel. We do not give a rule of thumb here.

Why would a clinic want a dedicated IP address on its VPN?

A dedicated IP gives the clinic one fixed address, so a system can be set to accept connections only from it. NordLayer says Core and above can add a dedicated-IP server for an extra monthly fee. Whether a given records system supports that is a question for its own vendor.

Do staff need single sign-on and multi-factor sign-in on a business VPN?

They are choices, not named product requirements. Single sign-on ties VPN access to your staff accounts, so removing a leaver in one place removes their access. Multi-factor sign-in asks for a second proof beyond a password. Proton says SSO is on its Professional plan, and NordLayer lists SSO and MFA.

Does a VPN replace the HIPAA risk analysis for a practice?

No. The Security Rule requires an accurate and thorough assessment of risks to patient data (45 CFR 164.308), and HHS says encryption alone cannot adequately safeguard it. A VPN is one control you may choose after that analysis. A VPN alone does not make a practice compliant.

Can a practice use a free or consumer VPN for patient records?

Do not assume so. The BAAs described above come with particular plans or billing terms, such as annual billing or an enterprise contract, and Proton’s scope for its VPN is unconfirmed. A free or consumer plan is not shown to come with one. Without a BAA, patient data should not cross it.